Query the data that can't move.
Core banking, payments, logs, CDRs. AlienGiraffe runs the query inside your network, next to the source. Raw rows never leave.
Sources, untouched
Sandbox, per request
Starts on approval, next to the source. Loads only the approved slice.
Approved consumers
Raw rows don't cross the line. Not to us, not to a cloud.
In Databricks' own words
Enterprises “cannot, and will not, move all of their data to the cloud.”
“Tier-1 banks have adopted ‘Hybrid Forever’ strategies.”
How people reach that data today
Every workaround costs something.
File a ticket
A DBA runs an extract. Weeks later a file lands on someone's laptop, often with the whole table.
1–4 weeks per request (IBM) ↗Copy it in
Pipelines copy the data into the cloud for good, with change capture running on your production database.
Query it remotely
Federation sends every query to production, and every result through cloud compute.
Alien Giraffe
Query it in place.
A short-lived sandbox next to the source loads only the approved slice.
- Rows stay in your network
- The source is read once per request
- Only the approved columns, rows, or time window
How it works
Ask for a slice, not a copy.
Requests name columns, row filters, and time windows. The source is read once per request, not once per query.
- 01
Request
Pick the datasource, then the tables, columns, and row filters you need. Templates turn repeat requests into one click, and can ask for a date window.
- 02
Approve
Approvers are set by role, by your admins. Low-risk requests can auto-approve. Each request shows a risk score from how many sources and fields it touches.
- 03
Sandbox
On approval, a short-lived sandbox starts inside your network, next to the source, and loads only the approved slice. The source is read once.
- 04
Query
People query in the explorer, in SQL or plain English. Apps, AI agents, and vendors connect through the API or MCP. Every query runs in the sandbox, not on production.
Governed the way you already govern
Your existing controls decide. The sandbox applies them at the source.
No new permission model to maintain. Identity, source grants, approvals, and catalog policy stay where they are today, and every sandbox inherits them.
Identity
People sign in through your identity provider
Single sign-on, with roles and organizations mapped from your IdP. Nobody gets a separate account to manage.
Okta, Microsoft Entra, and other SSO providers
Source grants
The source's own permissions are the ceiling
Each datasource is read with a login or role you grant and can revoke. A sandbox can never load more than that grant allows.
A read-only Oracle account, a Snowflake role
Approvals
Your teams decide who approves what
Approval rules by requester role, kept in a config file your team reviews. Low-risk requests can auto-approve, and the rule is recorded.
Catalog policy
Unity Catalog decides who may ask
The policies you already keep in Unity Catalog can govern data that never reaches Databricks. Open to design partners.
Unity Catalog, or the policy engine you run
Inside your network
One sandbox per approved request
- Loads only the approved tables, columns, and rows
- Never sees more than the source grant allows
- Read-only, and deleted automatically when access expires
Use cases
How teams use it.
Each one follows the same five beats: the situation, today's workaround, the request, what leaves the perimeter, and what the auditor sees.
A failed transfer, across the database and the logs
Five columns for one account and one day, plus one hour of API logs. One request instead of two tickets.
Read the storyMonthly product profitability on core banking
Selected columns, last full month. Forty follow-up queries hit the sandbox, not production.
Read the storyPlain-English questions over data that stays put
Network operations at a telco, claims triage at an insurer, quality at a plant.
Read the storyDesign partner program
Help shape governance for data that can't move.
We're selecting a small group of design partners in banking, telecom, and other regulated industries.
- Early access to Unity Catalog governance for on-prem data
- Direct input on which sources and policies come first
- Our engineers working alongside your platform and security teams
Backed by



Including the investors behind Drata and DataGrail, and the fund of Lookout founder Kevin Mahaffey.
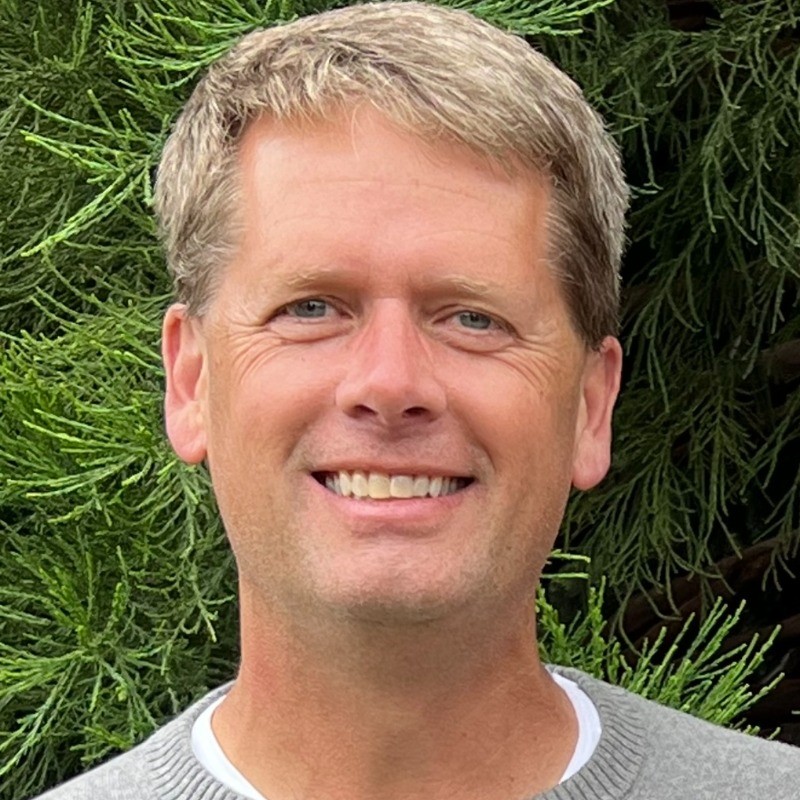
Advisor
Dave Hodson
Led authentication and authorization at Google Cloud and Microsoft.